A newly disclosed unfunded-channel flaw might go away Eclair, a Bitcoin Lightning implementation, crashing repeatedly with out an attacker spending BTC on-chain. The flaw affected reachable nodes operating v0.14.0 and earlier, with saved channel information making a restart inadequate to revive service.
Researcher Erick Cestari revealed the persistent-crash discovering Sept. 30 and defined it alongside a separate denial-of-service bug in an Oct. 1 developer put up. Each have been mounted in v0.14.1, launched in July, earlier than the general public disclosures. ACINQ now recommends the later v0.14.3 safety launch for separate vulnerabilities.
Why restarting might fail
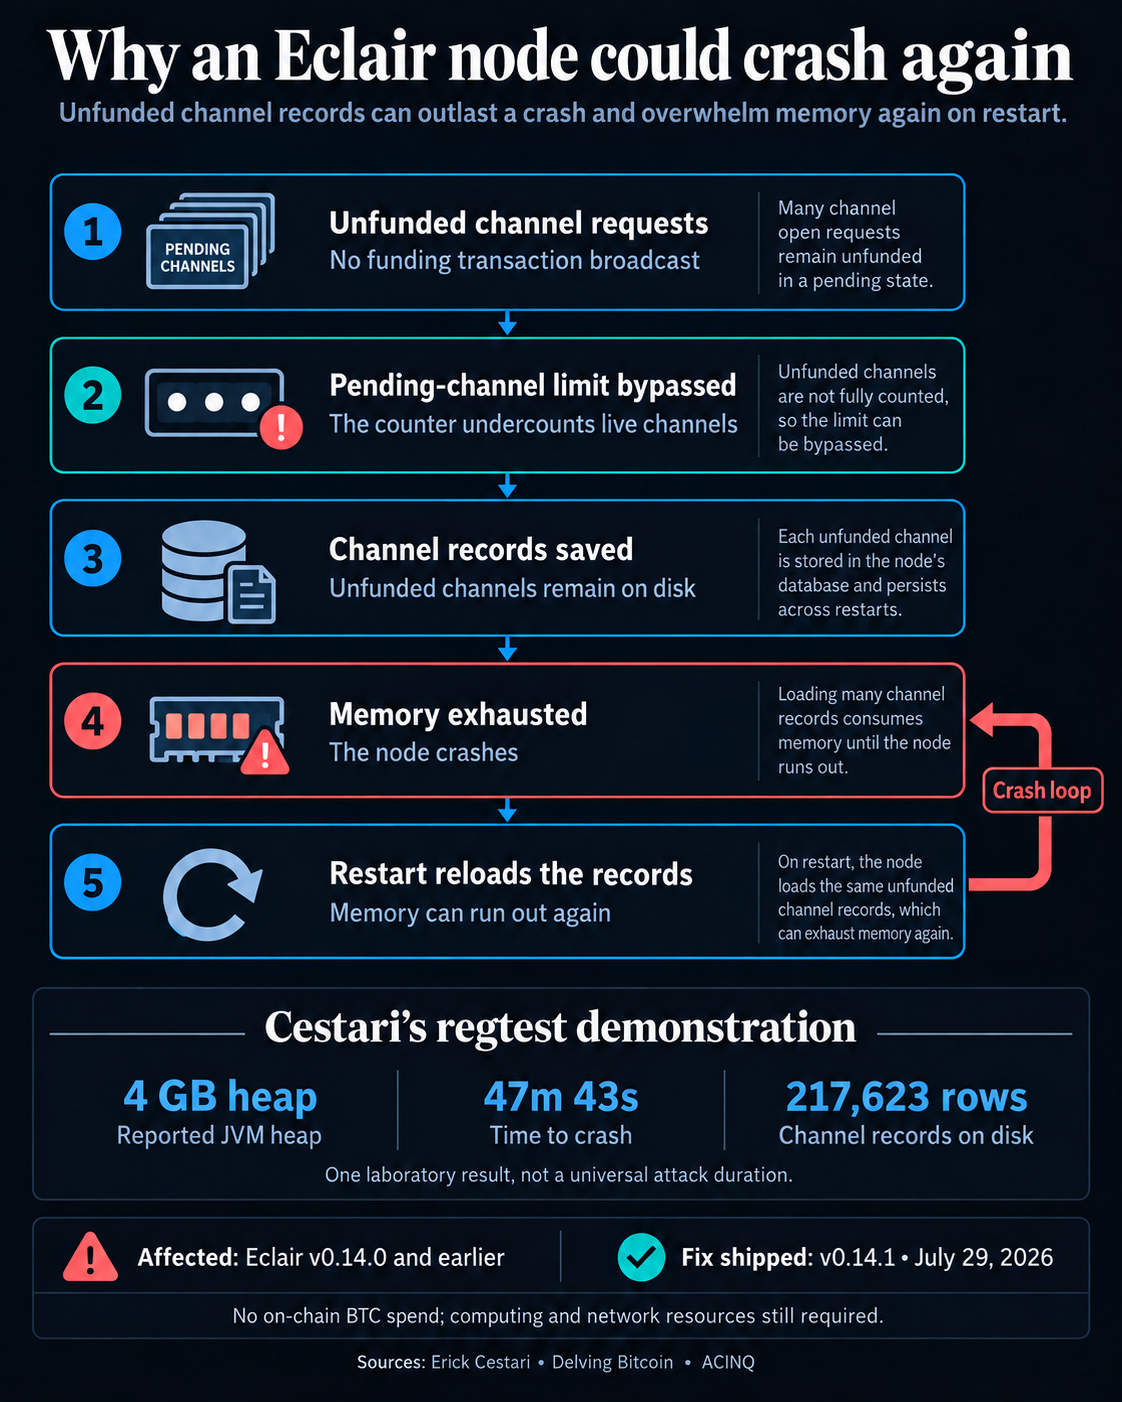
Eclair restricted the variety of pending channels a peer might open, however inconsistent checks of short-term and last channel identifiers let its counter undercount unfunded channels. A malicious peer might accumulate saved requests with out broadcasting the funding transaction or paying an on-chain price.
That distinction issues: the BTC usually wanted to fund a channel didn’t need to be dedicated for the susceptible node to incur reminiscence and database prices. The assault nonetheless required computing sources and community site visitors.
In Cestari’s proof of idea, Eclair v0.14.0 ran in regtest, Bitcoin’s native testing setting. He reported that the node exhausted a 4 GB Java digital machine heap after about 47 minutes 43 seconds, with 217,623 rows gathered within the channel database. That’s one laboratory benchmark, not a common assault length.
The preliminary crash left these information on disk. Throughout startup, Eclair reloaded the channels and exhausted reminiscence once more. Cestari described growing the heap or manually eradicating faux channel information as restoration measures. Repeated restarts left the underlying load in place.
The demonstration issues one susceptible node’s availability. It doesn’t set up reside exploitation or the variety of unpatched nodes.
ACINQ merged PR #3324 July 17. The patch strengthened duplicate-channel checks, and v0.14.1 shipped July 29. In accordance with Erick Cestari / Delving Bitcoin, v0.14.0 and earlier are affected, whereas v0.14.1 or later addresses these two denial-of-service findings.
The second bug, disclosed by Matt Morehouse / lnfuzz as LNF-2026-0003, was a channel-opening race that left orphaned channel processes consuming reminiscence or CPU. His advisory says the examined node recovered on disconnect or restart with out loss. That restoration consequence belongs to the race bug, quite than the persistent database flood.
These findings additionally differ from the fund-loss vulnerabilities yourcryptonewstoday coated Sept. 21, which have been patched in v0.14.3. The July minimal repair ought to due to this fact not be learn as a whole present safety suggestion.
ACINQ recommends upgrading to v0.14.3, launched Sept. 14, as a result of malicious nodes might exploit among the points it mounted. Stopping new unfunded-channel floods and recovering an already overloaded database are separate operator issues.