Bitcoin Core has added a safeguard towards signing transactions that will not bind funds to the cost vacation spot a consumer accredited.
The change, merged into Bitcoin Core’s grasp growth department on Sept. 25, targets a slender flaw in partially signed Bitcoin transactions, or PSBTs, that might produce a legitimate signature with out defending the supposed output.
Bitcoin Optech highlighted the replace on Oct. 2. The difficulty doesn’t expose a consumer’s non-public key, however creates a special danger: a signature can stay legitimate even when the transaction’s recipient is modified beneath particular circumstances.
The weak point entails SIGHASH_SINGLEwhich is a signing mode designed to commit an enter to the output within the corresponding place. If the transaction incorporates no output at that place, the safety breaks down in a different way relying on the kind of Bitcoin being spent.
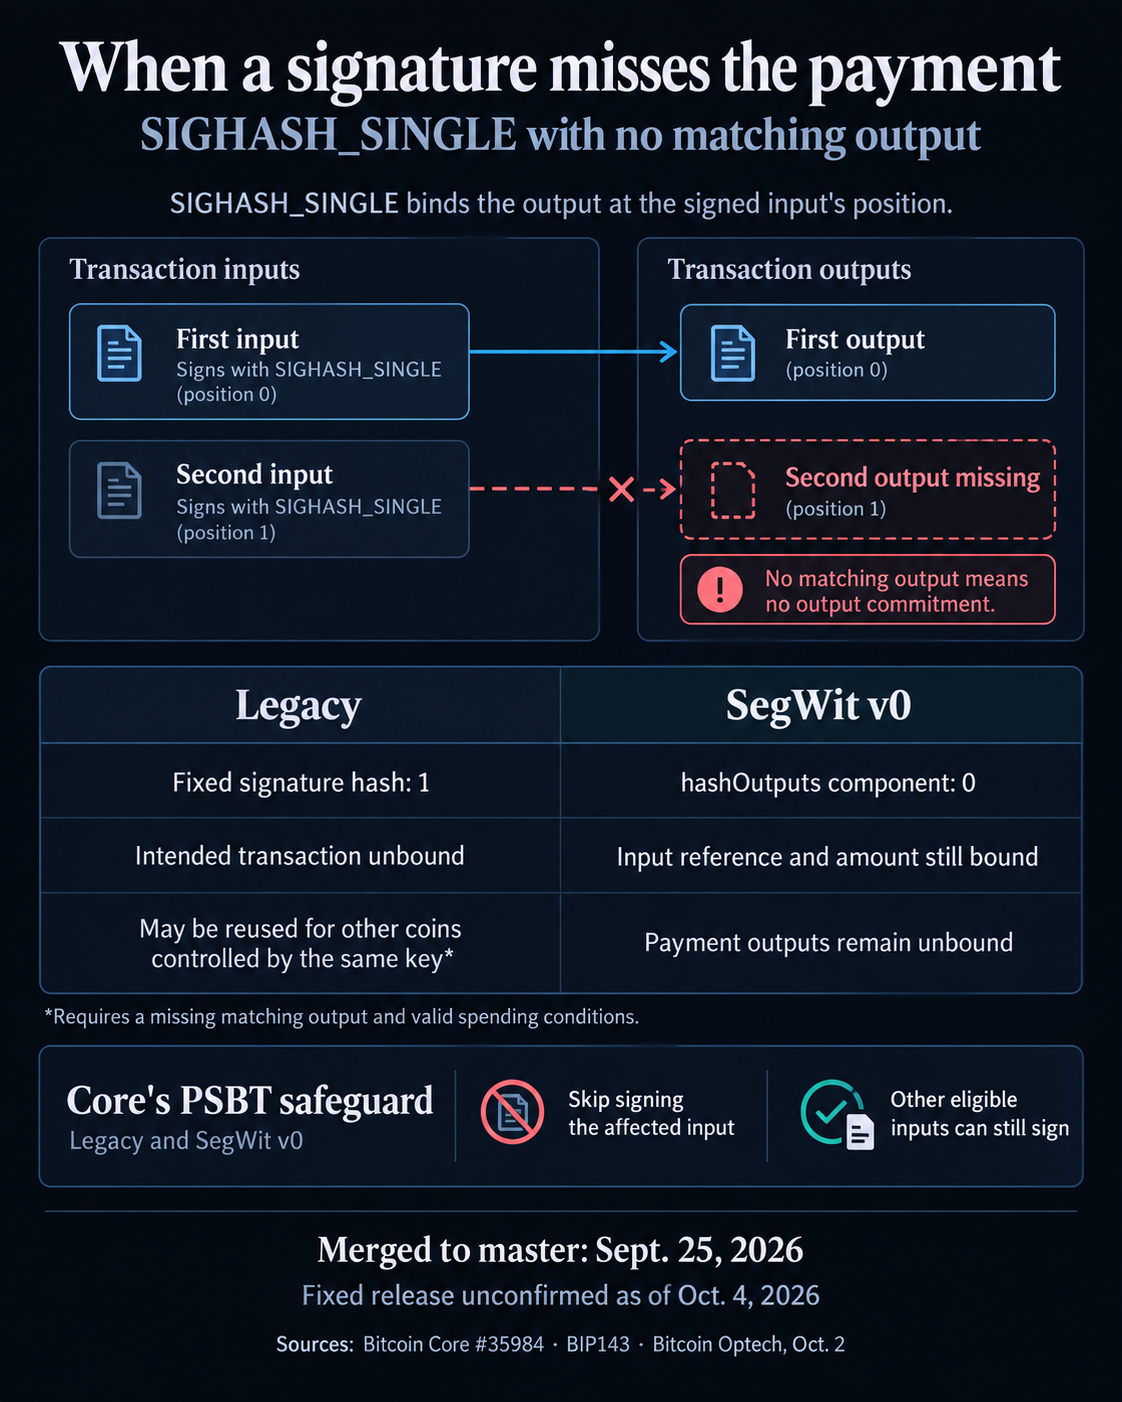
For legacy inputs, the missing-output case can produce a signature over a hard and fast hash worth. Bitcoin Core builders mentioned that signature might then be reusable towards different unspent outputs managed by the identical key when the identical structural circumstances are current.
SegWit v0 transactions retain stronger protections as a result of the signature nonetheless commits to the particular coin being spent and its quantity. The vacation spot output, nevertheless, can stay unbound.
That creates an authorization downside for wallets and signing gadgets: software program might current one cost to the consumer whereas producing a signature that doesn’t cryptographically assure that the accredited recipient stays unchanged.
Bitcoin Core blocks the dangerous signing request
Bitcoin Core already rejected the sting case by its raw-transaction signing interface. Its PSBT path, together with walletprocesspsbtmight nonetheless signal it.
The brand new code strikes the verify into Bitcoin Core’s shared signature-creation logic, stopping affected legacy and SegWit v0 inputs from being signed whereas permitting different legitimate inputs in the identical PSBT to proceed.
PSBTs are generally used to coordinate transactions between software program wallets, {hardware} gadgets and offline signers. They permit transaction builders to go info to a separate signer with out giving that system management of the non-public keys.
The repair due to this fact reinforces a boundary that pockets builders should implement independently of key safety: a legitimate cryptographic signature should decide to the transaction particulars the consumer truly approved.
Bitcoin Enchancment Proposal 174, which defines PSBTs, already tells signers to reject unacceptable signing modes and recommends SIGHASH_ALL when no different is specified. The Bitcoin Core change explicitly prevents this missing-output configuration from reaching the signing stage.
Customers don’t but have a confirmed manufacturing launch containing the safeguard. The Sept. 25 change was merged into Bitcoin Core’s growth department, whereas the mission’s printed launch listings had not recognized a hard and fast model or confirmed backport as of Oct. 4.
That leaves pockets suppliers and hardware-signing integrations with the extra quick determination: evaluation their very own dealing with of SIGHASH_SINGLE requests slightly than ready for a Bitcoin Core launch to implement the identical safety downstream.