Bitcoin Lightning developer ACINQ urged node operators to improve Eclair after patching safety flaws that malicious friends may exploit.
The corporate launched Eclair model 0.14.5 on Oct. 20, its second security-focused replace in 5 days, warning that a number of the newly addressed vulnerabilities may very well be exploited by hostile nodes. The software program powers Bitcoin Lightning nodes that keep cost channels and route transactions throughout the community.
The builders credited safety researchers Nuhiat-Arefin and mptfire with responsibly disclosing issues addressed within the replace.
The warning locations renewed strain on Lightning node operators, who keep Bitcoin-funded cost channels used to switch funds throughout the community. Vulnerabilities involving interactions with malicious friends create potential safety and operational dangers for infrastructure supporting Lightning funds.
Nevertheless, ACINQ has not detailed the newly patched exploit mechanisms or specified which older variations are affected. The announcement additionally reported no confirmed assaults or monetary losses, leaving the potential monetary penalties unclear.
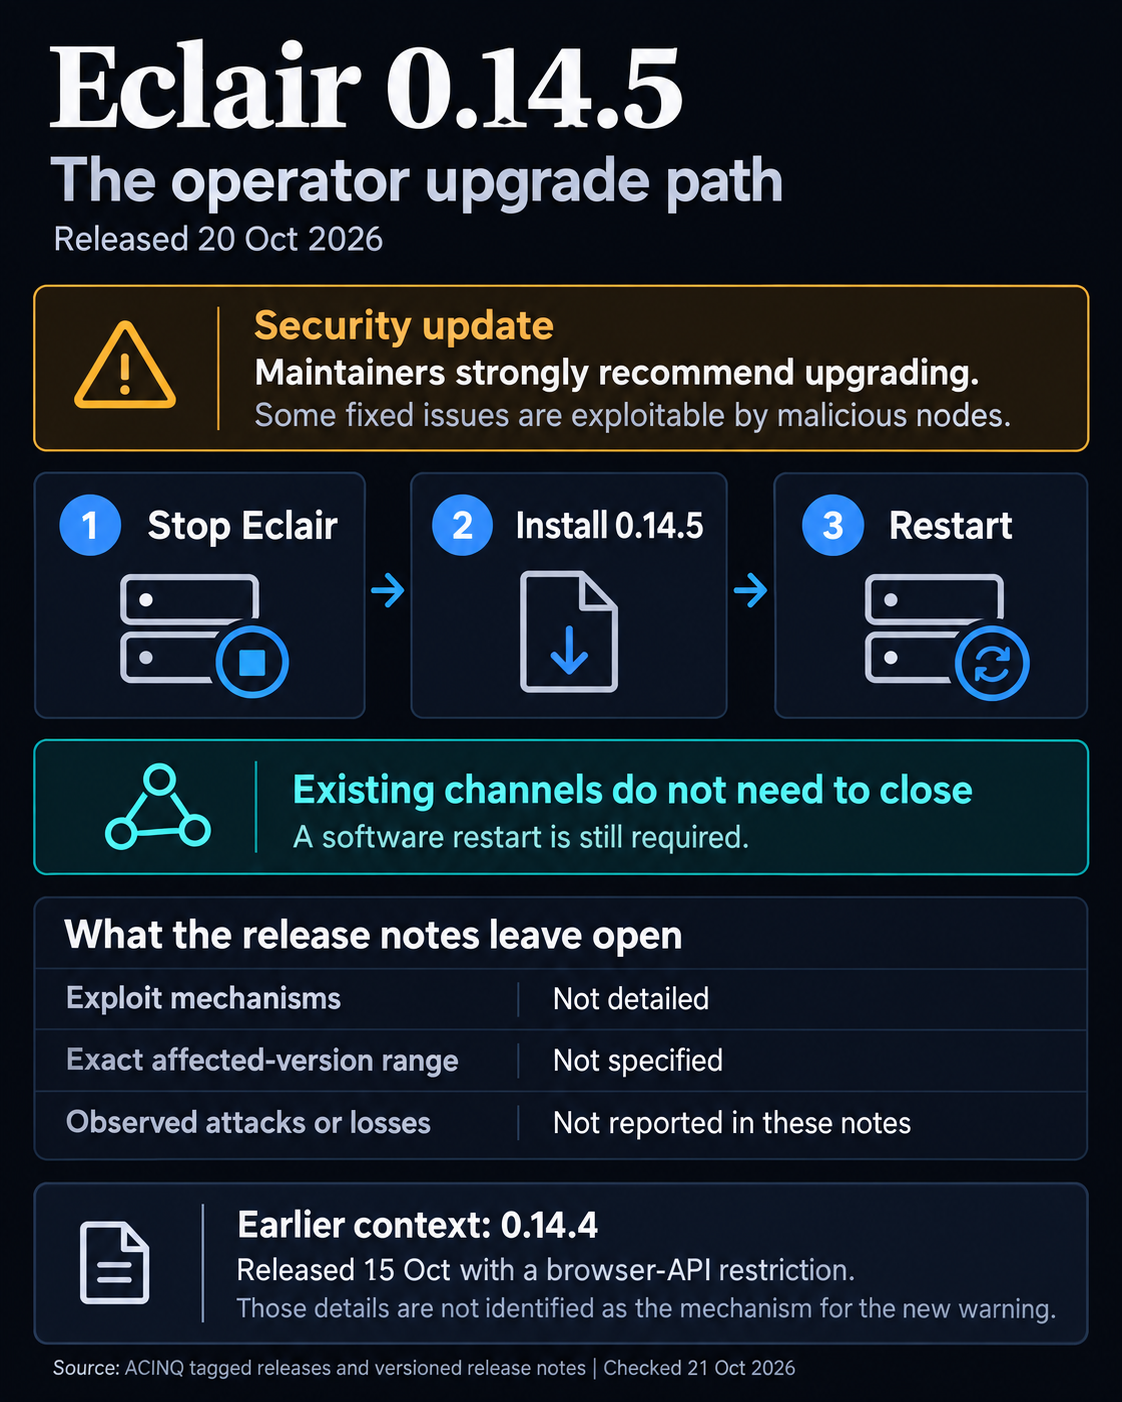
The builders have sought to reduce disruption from the improve. In line with the discharge directions, operators can set up the replace with out closing present cost channels.
As a substitute, they have to cease Eclair, set up the brand new model, and restart the software program. This avoids the blockchain transactions and channel reconfiguration that closing and reopening Lightning channels can require.
Eclair’s second safety replace in 5 days
The newest warning follows an Oct. 15 safety launch that launched further protections in opposition to malicious nodes and addressed a vulnerability involving Eclair’s administrative interface.
That earlier replace, model 0.14.4, blocked API requests carrying an Origin header, stopping direct browser entry to the software program’s software programming interface.
The builders defined that browsers may mechanically connect cached login credentials to cross-site requests. Because of this, a malicious web site a node operator visits may ship authenticated instructions to the node by a easy net type.
The change eradicated that assault route by rejecting browser-originated requests whereas preserving bizarre command-line entry.
Nevertheless, it additionally launched an operational requirement for companies and builders utilizing browser-based Lightning administration instruments. These interfaces now require an middleman backend to speak with Eclair’s API.
The newest launch extends the undertaking’s current safety work, though its maintainers haven’t linked the newly patched vulnerabilities to the beforehand documented browser challenge.
The successive updates additionally imply operators who put in the Oct. 15 launch should improve once more to acquire the protections launched 5 days later.
ACINQ has added safeguards to the set up course of, together with signed launch information and SHA-256 checksums that permit operators confirm downloaded software program earlier than deploying it.
These checks matter most for infrastructure dealing with Bitcoin-funded cost channels, the place putting in compromised software program may introduce dangers past the vulnerabilities being repaired.
Eclair 0.14.5 is now the undertaking’s newest launch, so operators in search of the most recent safety protections should full one other set up cycle.
The remaining query is how extensively older deployments are uncovered. ACINQ has not but printed an in depth vulnerability breakdown or listing of affected variations, leaving operators with no documented foundation to find out whether or not their present software program can safely stay in manufacturing.