An attacker would open a whole bunch of accounts, have every one provide a tiny quantity of a token in alternate for an unusually great amount of $XRP, then ship a single fee that purchased each provide directly.
The full $XRP owed could be too massive for the software program to rely appropriately, so the attacker’s promoting accounts could be paid in full whereas the shopping for account was charged virtually nothing — leaving the attacker with $XRP that hadn’t existed earlier than.
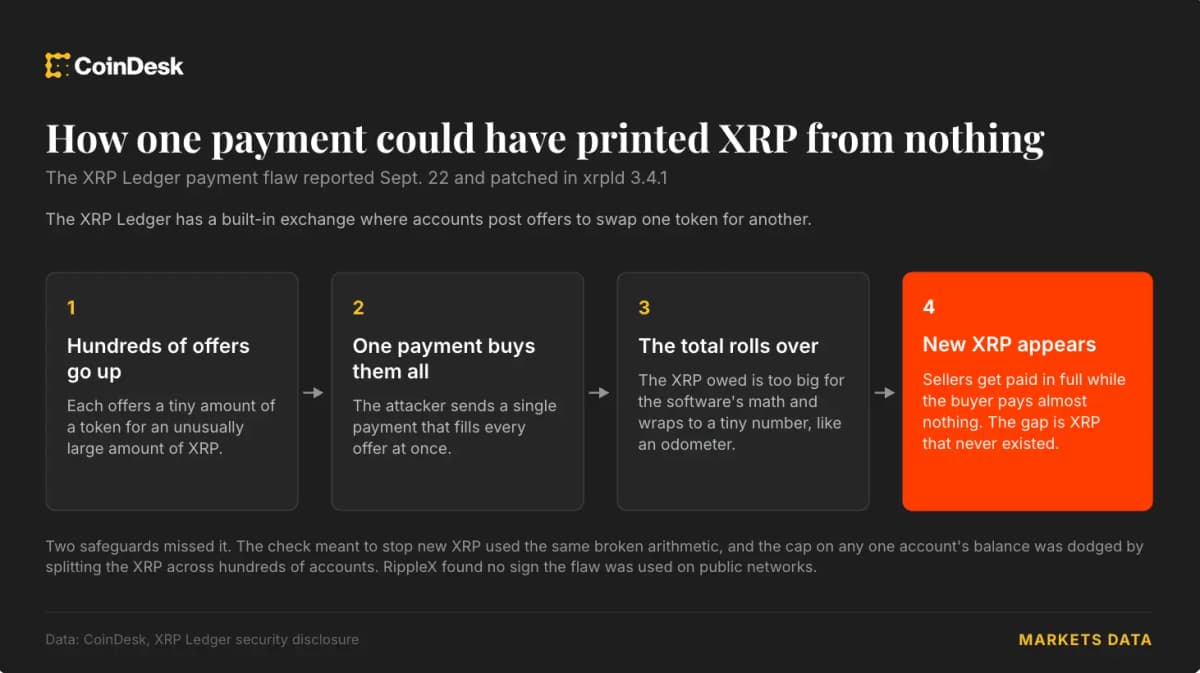
The $XRP Ledger runs a test after each transaction to ensure no new $XRP has appeared, however that test relied on the identical miscounted whole and would have missed it. A separate restrict on how a lot $XRP a single account can obtain wouldn’t have triggered both, as a result of the assault unfold the $XRP throughout a whole bunch of accounts.
The researchers’ technique wanted just a few hundred $XRP to open these accounts, most of which may very well be recovered, plus transaction charges.
Builders shipped the repair in xrpld 3.4.1, the ledger’s server software program, on Sept. 25 with out disclosing what it repaired.
The incident joins a run of long-hidden crypto safety flaws surfaced with AI assist since July, together with the Coldcard pockets bug behind the theft of a minimum of 1,367 BTC and the vulnerabilities that pressured Core Lightning to inform bitcoin node operators to disconnect.