Withdrawals from SIG Community’s experimental Ethereum vault require its signing community, despite the fact that the underlying belongings keep on Ethereum. The instance illustrates the withdrawal dependency in Midnight’s Nightmode privateness plan: customers burn a shielded declare earlier than the exterior switch is signed, and failed-transfer restoration additionally wants an attested response.
Charles Hoskinson’s @IOHK_Charles account welcomed Tron to Midnight on Oct. 21. SIG’s roadmap targets Tron for December 2026, whereas its listed Ethereum integration is on the stagenet take a look at community.
How the Ethereum vault holds belongings
SIG describes its service as giving a Midnight contract an extraordinary Ethereum account. A threshold of signers produces the Ethereum signature when the contract requests it. SIG says the signers are unbiased and that no single signer can act alone.
On this instructional and experimental software, the underlying ERC20 tokens sit within the vault’s EVM account. On Midnight, customers maintain shielded vault tokens representing their claims on that pool. Native belongings staying on Ethereum subsequently solutions the place the belongings are recorded; it doesn’t, by itself, reply who could make them transfer.
The excellence additionally explains the burn. Beginning a withdrawal destroys the shielded declare being redeemed, fairly than destroying the underlying ERC20. A profitable exterior fee finishes the redemption. If the fee receives one of many documented failure outcomes, the appliance can restore the declare.
The withdrawal walkthrough treats the holder’s coin spend as authorization. The holder provides a shielded vault coin matching the token and actual withdrawal quantity, then chooses a vacation spot deal with. The circuit rejects a zero vacation spot.
The startWithdraw circuit burns that coin and queues the request. A later queue flush assigns the vault account’s transaction sequence quantity, often called its nonce. The ship step then data a request for the precise ERC20 switch and notifies the MPC, or multiparty computation, signing service.
The remainder is a sequence of distinct tasks:
| Step | What should occur | Withdrawal consequence |
|---|---|---|
| Authorize and queue | The holder spends the shielded declare; Midnight data the request. | The declare is burned earlier than the exterior payout. |
| Signal | The MPC service returns a signature for the vault’s switch. | The holder’s authorization alone can’t signal from the vault account. |
| Broadcast and execute | The consumer submits the signed transaction; Ethereum processes it. | A returned signature nonetheless wants an exterior transaction to execute. |
| Attest | The MPC service experiences the transaction’s final result. | Midnight settlement is dependent upon an authenticated final result. |
| Full | The vault checks the settlement report and closes the request. | The consequence determines whether or not the shielded burn stands or the declare is re-minted. |
The signing service doesn’t broadcast the transaction. The dApp or relayer assembles it with the verified signature and sends it to the EVM chain.
A failed switch and a silent service are completely different
The service has a second job after signing. It provides an attestation of the exterior transaction’s final result, separate from the signature that licensed that transaction. The mixing protocol describes binding that final result to the request and its returned knowledge.
The vault checks the attestation in opposition to its configured MPC response key earlier than permitting settlement.
The withdrawal specification describes 3 ways the declare will be restored: a reverted transaction, a transaction made unviable as a result of one other consumed its nonce, or an executed ERC20 switch that returned false. After the attested result’s queued and flushed, the withdrawer completes the request and receives a re-minted shielded quantity.
A profitable switch returning true leaves the burn in place and closes the request. On the failure path, the restoration is a vault declare on Midnight, fairly than a brand new fee of the native asset to the vacation spot.
The documented refund route requires a verified, flushed attestation. An unanswered signing request or a lacking final result response doesn’t itself meet that situation.
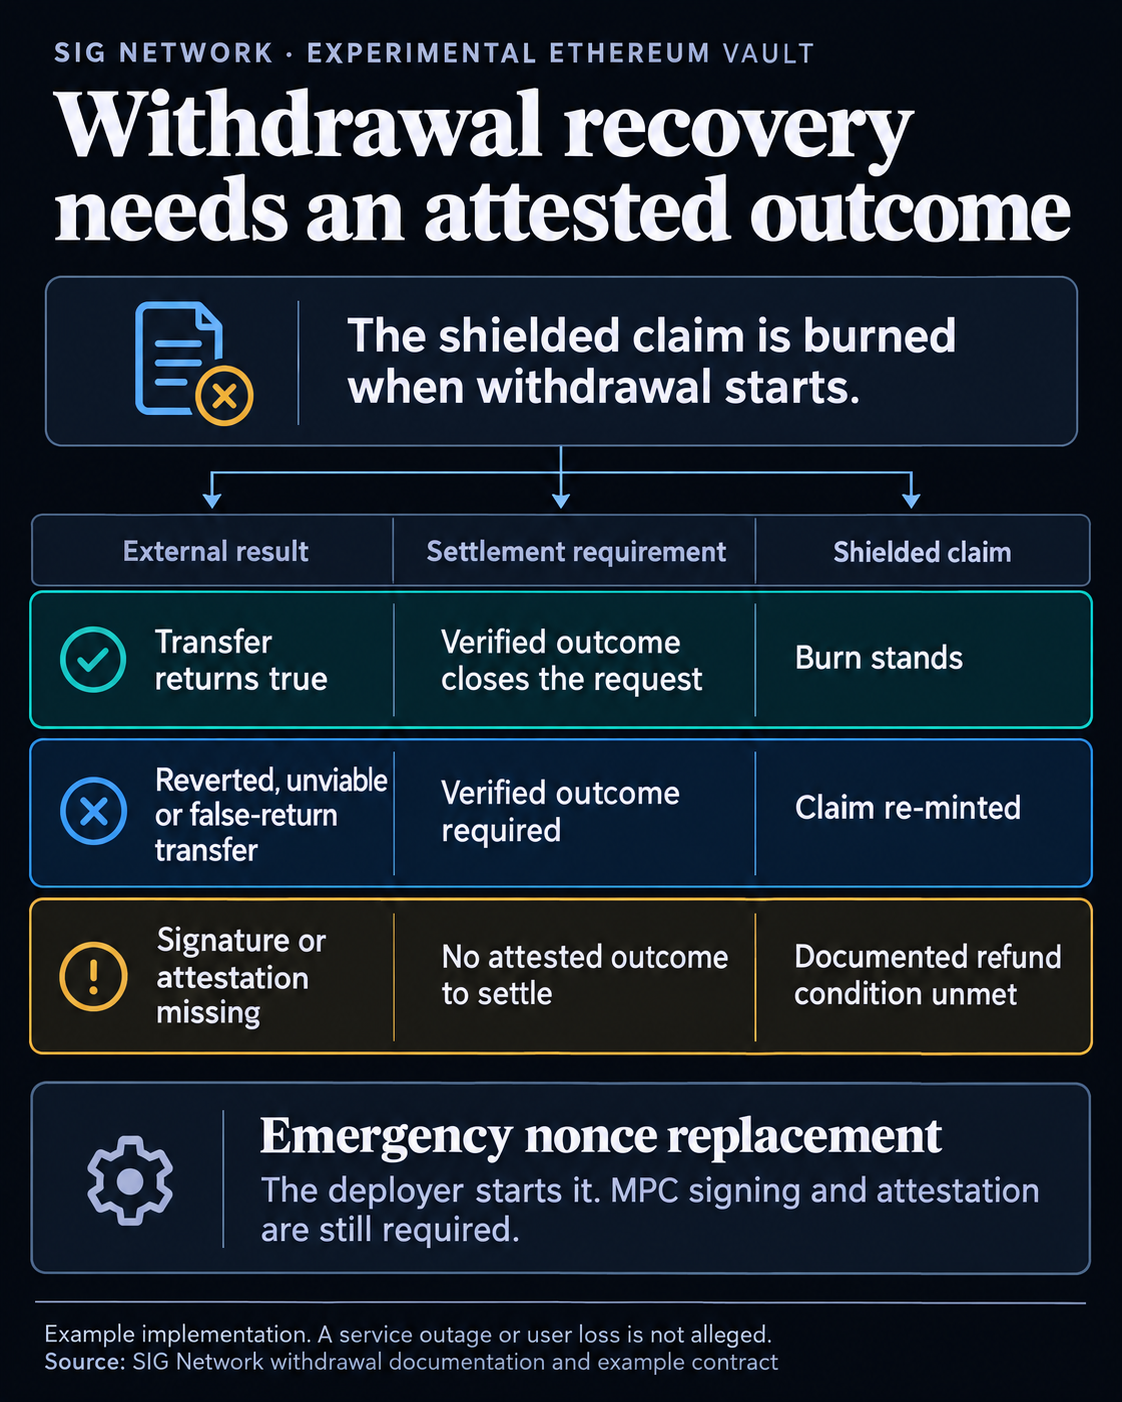
The instance additionally has an emergency mechanism within the vault code. The deployer can begin a nonce-replacement request for a caught vault transaction, utilizing a zero-value switch from the vault account again to itself on the identical nonce.
The aim is to make the unique transaction unviable, after which an attested final result can assist its failure settlement. Beginning this restoration is restricted to the deployer, though sending an already-fixed request is permissionless. It’s one other signed transaction, adopted by attestation, fairly than an exit that bypasses the MPC service.
The code additionally carries a particular warning: changing an unique request earlier than the MPC has signed it could race that request, probably leaving it with out an attestation and its surrendered shielded declare burned.
The deployer additionally units the preliminary account, chain and response-key configuration and may change the vault’s fuel settings. Already-started requests retain the fuel values copied after they started.
The manufacturing take a look at is the entire exit path
Mainnet assist stays tied to ledger v9 on SIG’s roadmap. The Oct. 21 repository replace prepares vault package deal 0.5.0 on SIG Midnight 0.25.0. At that code model, the revealed deal with registry accommodates a stagenet vault deal with and a clean mainnet entry, which the file defines as not but deployed or revealed.
SIG’s separate full-stack demo makes use of Midnight stagenet and Ethereum Sepolia, each public testnets, with a “fakenet” MPC responder. That demonstrates an software move. It doesn’t set up {that a} manufacturing quorum of unbiased signers is working that demo.
SIG’s threshold-signing description addresses how a signature is produced. Evaluating an precise deployment additionally requires figuring out what number of signers should cooperate, who operates them, how these preparations can change and what restoration can full when extraordinary service is unavailable.
Audit scope wants the identical precision. Hacken’s ultimate report dated Feb. 21, 2025 covers Ethereum Solidity chain-signature contracts. Its scope doesn’t set up protection of the newer Compact vault or the entire Nightmode system.
The subsequent deployment proof is subsequently extra consequential than one other enlargement announcement: the precise manufacturing code and addresses, its signing and attestation configuration, audit protection for these parts, and a restoration path matched to service failure.