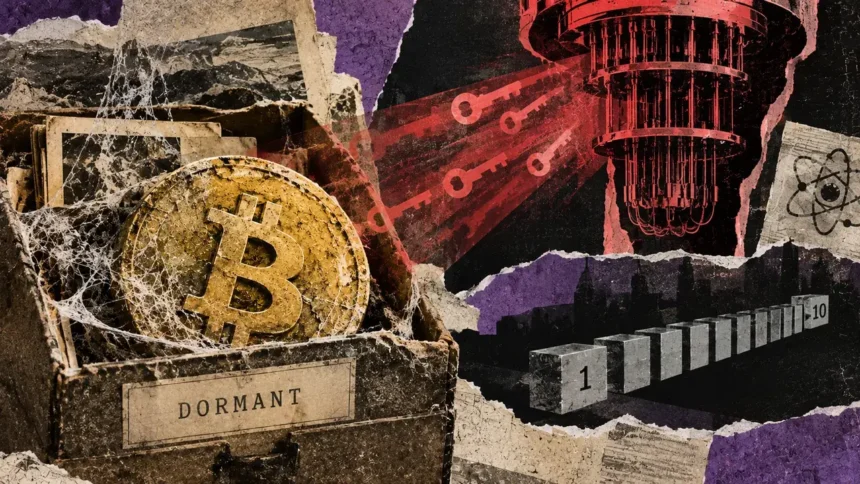
Crypto investor Nic Carter’s worst-case quantum state of affairs consists of a hostile actor recovering the keys to dormant Bitcoin, then broadcasting a wave of spends throughout 10 blocks.
In his Oct. 13 interview with Luke Martin, Carter says early cash shifting collectively may shake confidence within the community.
The stakes lengthen past selecting stronger cryptography. Glassnode’s Could 20 evaluation recognized 6.04 million BTC, or 30.2% of then-issued provide, with public keys already uncovered.
The state of affairs assumes a future quantum machine able to breaking Bitcoin’s key cryptography. Google’s printed analysis fashions future assets for such an assault, and Bitcoin key restoration stays undemonstrated in that work. Giant early outputs can nonetheless make a fast switch attainable on block-space grounds.
Can hundreds of thousands of BTC slot in 10 blocks?
A sufficiently highly effective quantum laptop may use Shor’s algorithm to recuperate non-public keys from uncovered public keys, gaining the flexibility to authorize spending. Early pay-to-public-key (P2PK) outputs reveal these keys straight.
An attacker may work privately, withholding transactions till prepared, as Bitcoin Enchancment Proposal 361 (BIP-361) explains.
Bitcoin tracks funds in particular person unspent outputs, every with its personal spending circumstances, and a switch’s dimension is dependent upon what number of outputs it consumes and their kind.
Take into account an explicitly hypothetical set of fifty,000 early outputs holding 50 BTC every, totaling 2.5 million BTC altogether. Utilizing the Bitcoin developer reference’s P2PK enter instance, these inputs require about 5.7 million bytes, equal to 22.8 million weight models earlier than transaction overhead.
Ten blocks have an mixture ceiling of 40 million weight models below Bitcoin’s block-weight guidelines. With one compact receiving output per batch, the illustrative set suits beneath that ceiling, together with overhead, when break up into transactions beneath Bitcoin Core’s 400,000-unit customary weight restrict.
An precise sweep’s block-space demand would rely upon its explicit outputs and spending necessities.
Charges, competing visitors, and miner choices nonetheless decide inclusion. Affirmation follows solely when miners embody the transactions. With Bitcoin’s roughly 10-minute block interval, 10 blocks common roughly 100 minutes, with substantial variation.
Glassnode’s publicity measure contains lively holdings whose keys grew to become seen by earlier spending or deal with reuse, alongside structurally uncovered outputs resembling P2PK and Taproot.
Public-key publicity, holder inactivity and everlasting key loss are separate questions, as is attribution to Satoshi Nakamoto.
In his Could 21 evaluation, safety researcher Jameson Lopp estimated that about 2.6 million uncovered BTC is perhaps unable emigrate, utilizing inactivity and known-entity labels as proxies.
A quantum sweep would switch management of present cash with out creating extra issuance. A visual switch may unsettle holders earlier than a sale, whereas trade responses and liquidity circumstances would decide any subsequent market disruption.
Who may nonetheless show Bitcoin possession?
Holding present spending guidelines intact preserves the flexibility to spend with a legitimate key, together with one a future attacker recovers. Proscribing legacy signatures adjustments that discount: house owners who can’t migrate or meet rescue circumstances may lose entry.
Draft BIP-360 proposes Pay-to-Merkle-Root, a brand new output kind with out Taproot’s uncovered key spending path. It could scale back long-exposure threat when keys keep hidden.
BIP-361 proposed phases would limit new susceptible locations about three years after activation, then tighten legacy-signature spending by rescue circumstances about two years later.
For comparability, Google’s 2029 goal units its personal precautionary migration deadline.
One potential rescue depends on a father or mother secret in a pockets that makes use of hardened key derivation. An attacker recovering a person spending key would ordinarily lack that extra secret. For naked P2PK outputs, the draft’s authors describe that form of possession proof as an unresolved downside.
Dan Robinson’s Could 1 PACT idea explores superior, non-public timestamps proving deal with management. Future guidelines may acknowledge that proof after a legacy sundown, and its safety is dependent upon the holder making ready earlier than quantum key restoration turns into attainable and preserving the proof, alongside standardization and adoption of future verification guidelines.
The February Hourglass V2 draft takes one other strategy: one P2PK spend and one BTC of web spending per block. Throttling would sluggish the outflow whereas constraining professional holders below the identical guidelines.
These stay proposals and analysis ideas. Their trade-offs embody continued publicity, restricted entry, and unequal restoration choices.
Below the BIP course of, Bitcoin’s individuals consider and undertake proposed adjustments by software program and ecosystem acceptance.
Carter’s state of affairs brings the important thing selection into focus: safer locations can defend holders who can transfer. Bitcoin’s neighborhood would nonetheless should determine which claims to acknowledge when an atypical signature can now not distinguish an authentic holder from a quantum attacker.