Safety flaws throughout main x402 fee facilitators might expose facilitator-held property and go away retailers with out receiving fee for providers supplied, in keeping with new analysis introduced on the thirty fifth USENIX Safety Symposium.
Researchers examined 15 main x402 facilitators, together with Coinbase, Thirdweb, PayAI and Mogami, and located that each platform violated at the very least one safety rule.
They mapped 49 rule violations to 31 distinct vulnerabilities throughout techniques that accounted for 99% of noticed x402 transactions and 98% of fee quantity in the course of the research.
The researchers recognized 4 broad assault courses, together with free purchasing, asset theft, service disruption, and gasoline abuse.
They straight validated six assault paths below bounded circumstances, together with two free-shopping assaults, three gas-abuse assaults, and one path that would expose facilitator-held property.
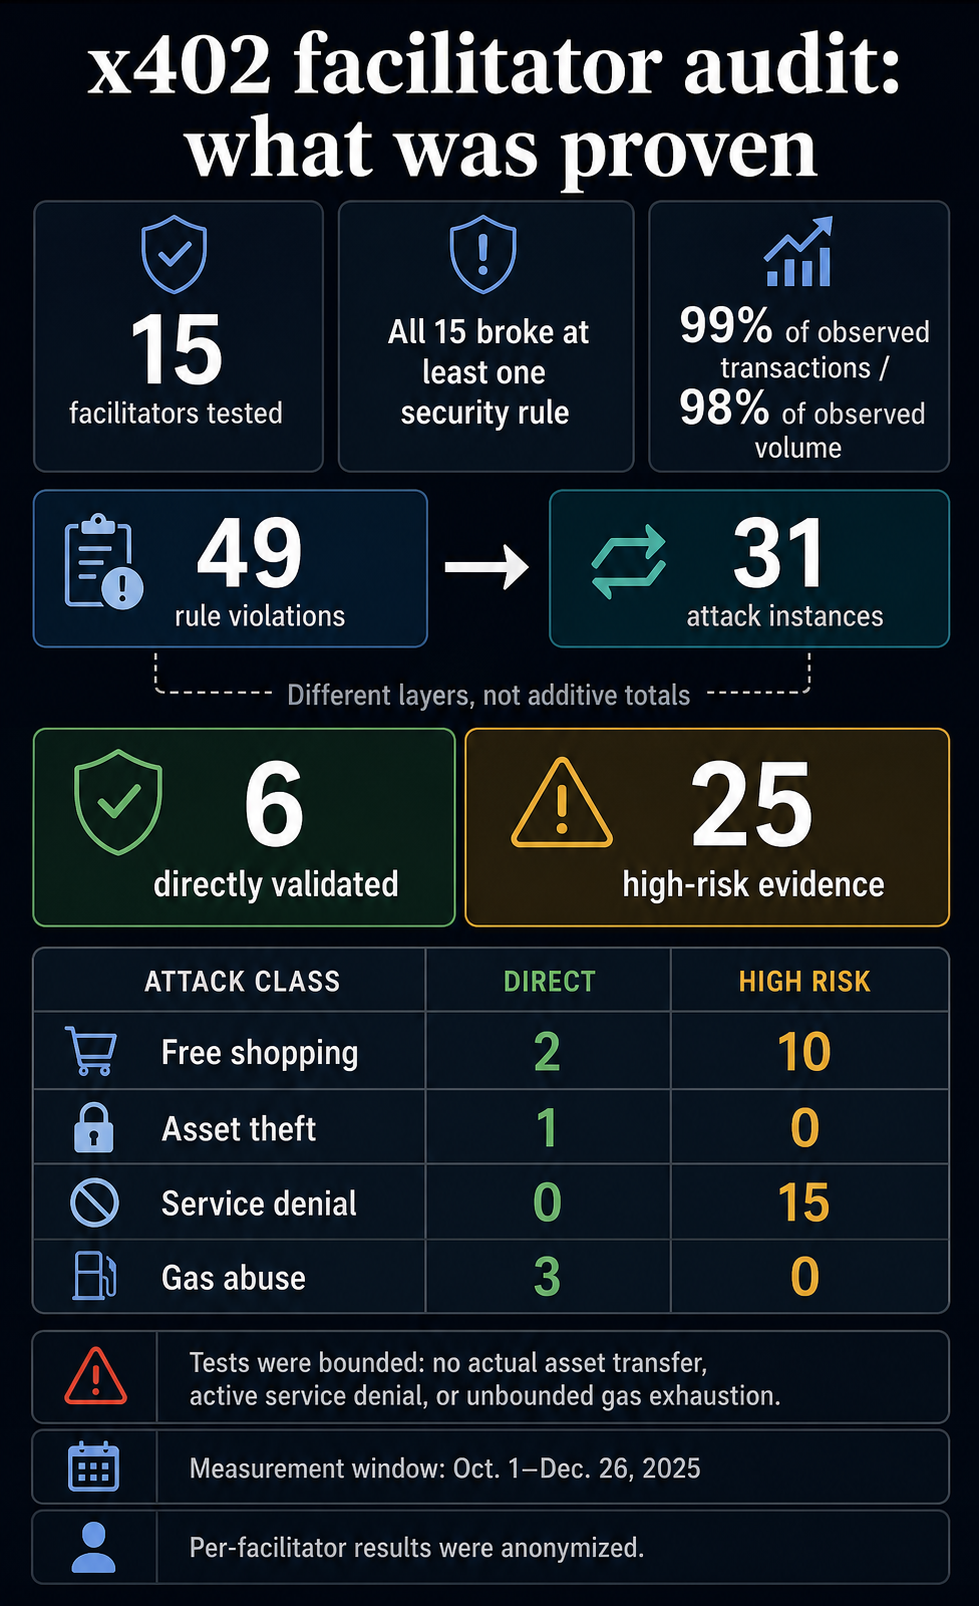
The findings don’t imply that 99% of x402 transactions have been themselves weak. Quite, the paper mentioned the assaults might trigger “direct monetary loss to retailers, theft of facilitator-held property, unbounded sponsor-paid gasoline/charges, and disruption of fee providers.”
The findings come as x402 is being promoted as infrastructure for machine-driven commerce, permitting web sites and APIs to request funds that software program and AI brokers can full autonomously. Facilitators sit between patrons and retailers, checking signed fee authorizations earlier than submitting transactions to blockchains.
That place offers facilitators vital management over settlement whereas additionally concentrating danger.
Facilitator funds might be uncovered
Probably the most extreme assault path concerned ERC-6492, an Ethereum signature customary designed to help signatures from smart-contract wallets that will not but have been deployed.
Researchers discovered that malicious metadata might trigger a facilitator to fund and submit an arbitrary token-approval transaction somewhat than the fee it anticipated to settle.
The researchers stopped in need of shifting facilitator funds, however categorised the flaw as a direct path to asset theft as a result of an attacker might probably use that authority to approve transfers of property managed by the facilitator.
Three different validated assaults exploited the identical financial characteristic that makes facilitators helpful to retailers: facilitators can sponsor blockchain transaction charges on their behalf.
Attackers might drive affected implementations to pay for costly smart-contract deployment or initialization, shifting probably unbounded community prices onto the facilitator.
“If facilitators sponsor charges with out dependable reconciliation or chargeback, attacker-induced settlement can change into direct sponsor loss,” the researchers wrote.
That publicity is already seen in regular settlement exercise, though the research didn’t set up that historic failures have been malicious.
Researchers analyzed greater than 119 million x402 transactions throughout Base and Solana between Oct. 1 and Dec. 26, 2025. Facilitators spent about $202,000 on community charges, together with roughly $5,800 on Base transactions that in the end reverted or failed.
The failed transactions present the financial asymmetry constructed into sponsored settlement: a facilitator can incur blockchain prices even when the fee itself by no means completes.
Retailers can launch providers earlier than fee lands
A second group of flaws creates the alternative drawback, shifting losses from facilitators to retailers. The researchers dubbed the assault “free purchasing.”
An x402 fee can move an preliminary off-chain verification however nonetheless fail when submitted to the blockchain, together with as a result of an authorization has expired or the customer not has ample funds.
If a service provider releases an irreversible service instantly after verification, the customer can obtain the product though settlement later fails.
Researchers straight validated two free-shopping assault paths and categorised one other 10 as excessive danger.
The issue prolonged past particular person facilitators to software program provided to retailers. All seven official Coinbase reference server kits examined by the researchers lacked specific mechanisms for reversing actions taken after a profitable verification.
In variations of Coinbase’s Flask equipment by way of 0.2.1, protected assets might be launched after verification no matter whether or not the following settlement succeeded.
That design is very consequential for AI-driven commerce, the place autonomous software program could request and eat APIs, knowledge, or different digital providers inside seconds. McKinsey has estimated that AI brokers might mediate $3 trillion to $5 trillion of worldwide shopper commerce by 2030.
Coinbase dominates a concentrated facilitator market
The potential blast radius is amplified by the focus of x402 exercise in the course of the researchers’ measurement window.
Coinbase was the biggest facilitator by a large margin, processing 77.17 million transactions and practically $27 million in fee quantity.
Focus additionally appeared on the service provider facet. Greater than 93% of the roughly 53,500 distinctive servers noticed within the research have been related to a single facilitator.
That construction creates a vulnerability, outage, or flawed software program assumption at one massive supplier that may have an effect on 1000’s of retailers somewhat than stay remoted to a small implementation.
It additionally makes remediation uneven. Fixing a facilitator’s core service could not get rid of publicity if retailers proceed operating older software program growth kits or launch merchandise earlier than settlement finality.
Fixes have began, however deployment stays unclear
The disclosures have prompted remediation by a few of the facilitators examined, although the general public document doesn’t present how extensively these fixes have been utilized to reside x402 infrastructure.
The paper’s newest remediation replace, dated Feb. 6, mentioned Coinbase, PayAI and Mogami had collectively confirmed six vulnerabilities. Some had been fastened, whereas work continued on others.
The researchers didn’t publicly map particular person vulnerabilities to particular facilitators, making it tough to find out which suppliers have been uncovered to every assault or how broadly fixes have reached manufacturing techniques.
As a substitute, they really useful treating all client-provided transaction fields as untrusted, rechecking fee circumstances instantly earlier than settlement, and imposing strict limits on facilitator-sponsored gasoline prices.
For retailers, the researchers really useful withholding irreversible providers till settlement succeeds or sustaining a strategy to reverse actions when fee fails.
These safeguards deal with the assault paths recognized within the research. Their effectiveness will rely upon whether or not facilitators, SDK builders, and retailers deploy them constantly throughout an x402 market whose exercise is already concentrated amongst a small group of suppliers.