The location for house owners to get better their NFTs has gone stay, in keeping with the whitehat that launched the rescue mission to avoid wasting at-risk NFTs throughout the safety incident the place 2024-era Magic Eden customers have been uncovered attributable to an exploit of Restrict Break’s Cost Processor.
A part of the situations for house owners to reclaim their NFTs, in keeping with 0xQuit, the vice chairman of blockchain researcher at Yuga Labs, who ran the rescue mission, is that they first revoke the outdated, problematic approval.
The restoration course of is totally free as properly, with solely normal gasoline charges utilized.
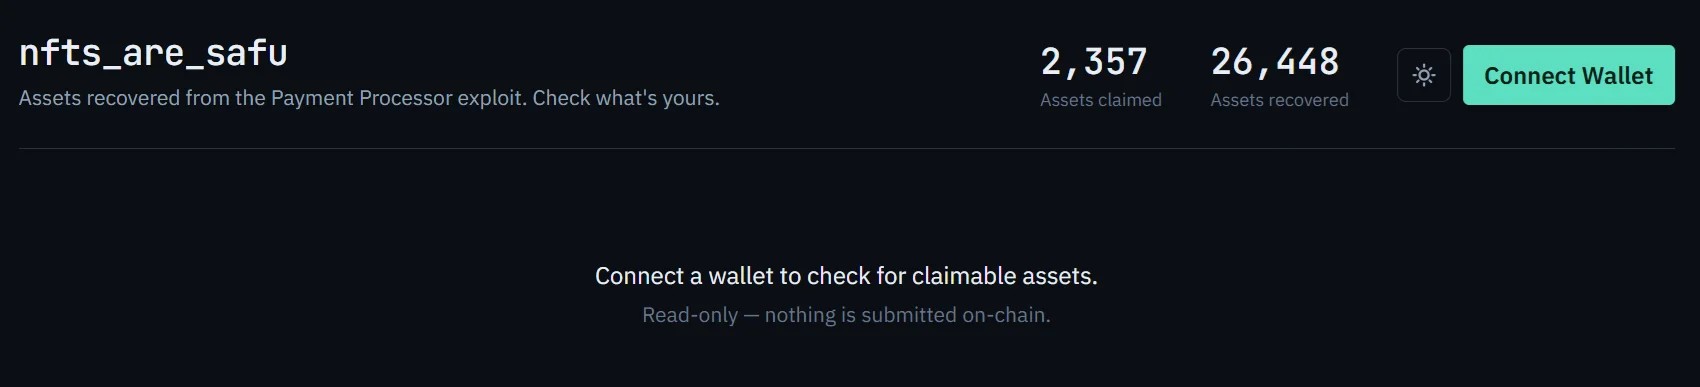
Notably, solely rescued NFTs will be reclaimed from the positioning, whereas these in possession of the exploiters usually are not recoverable, as of this Cryptopolitan report.
The way to reclaim rescued NFTs
0xQuit declared the restoration web site open late on Saturday, writing on X, “Declare web site is stay. If I used to be in a position to save your NFTs, now you can reclaim them,” he wrote on X.
To keep away from repeat publicity, the Yuga Labs govt warned that $NFT house owners can solely reclaim their NFTs after they revoke the Cost Processor approval that brought about the entire incident within the first place.
Revoke.money additionally warned that the assault depends solely on the approval, so canceling listings is ineffective at stopping the exploit.
nftsaresafu.xyz is the one official web site, and as of publication, 2,357 have already been claimed out of the 26,448 recovered property.
0xQuit additionally warned that the declare interacts with a delegated pockets setup, which might intrude with transaction simulation in some wallets.
How a 2024 approval virtually brought about an $NFT catastrophe
The September 2026 exploit has roots that return so far as an $NFT buying and selling protocol that Magic Eden adopted in 2024 to settle EVM trades, Cost Processor V2. Nevertheless, in keeping with Revoke.money, when Magic Eden dropped the processor constructed by Restrict Break in October 2024, the token and $NFT approvals customers granted throughout that interval have been by no means turned off on-chain.
That energetic permission was what the attacker exploited, utilizing it to hijack NFTs outright and to purchase nugatory NFTs utilizing tokens saved in wallets.
Not less than $2.8 million has been stolen for the reason that exploit started on September 24, affecting wallets on Ethereum, Polygon, Base, Arbitrum, and ApeChain.
As a result of V2 can’t be paused or patched, it stays susceptible indefinitely. Restrict Break paused the newer V3 all over the place besides ApeChain, the place it stays usable till November 30, 2026.
What the whitehats saved, and what they couldn’t
0xQuit mentioned the assault surfaced after somebody abused the bug to steal 10 Meebits, 50 Otherdeeds, 10 World of Girls NFTs and 235 Determined ApeWives, and that it took greater than 12 hours earlier than anybody flagged it to him.
As soon as he grasped the scope, safety researchers used the identical flaw defensively to maneuver at-risk property right into a pockets beneath their management. The operation reportedly rescued 23,155 NFTs value greater than $5.7 million.
Not every thing might be reached in time. “660 WETH was in danger, which we sadly weren’t quick sufficient to get better,” 0xQuit advised The Block, explaining that the exploit might be run in reverse to tug WETH.
Particular directions for sure $NFT collections
Some collections won’t launch cleanly. 0xQuit warned that holders of ERC721C or ERC1155C collections could also be unable to say due to switch validator guidelines, and requested affected assortment house owners to regulate their settings or allowlist the positioning. He mentioned he would work via these circumstances over the approaching days.
Magic Eden mentioned no stay listings have been hit and that it closed its EVM market within the first quarter of 2026. {The marketplace} suggested customers to revoke the V2 approval on Ethereum, Polygon, and Base. In the meantime, OpenSea co-founder Chris Maddern mentioned his workforce had flagged greater than 3,000 gadgets as stolen to dam resale.
Occasions like this draw scammers. Cryptopolitan has beforehand reported that pretend “restoration” and “declare” websites are likely to observe high-profile exploits, so customers ought to attain the declare software solely via 0xQuit’s verified submit and revoke approvals via a trusted checker somewhat than hyperlinks despatched by strangers in DMs or replies.