- Ledger CTO Charles Guillemet revealed a technical evaluation on September 16, 2026, evaluating the SHRINCS post-quantum signature proposal.
- The SHRINCS draft specifies signature sizes starting from 548 to five,777 bytes, in comparison with the 64 to 72 bytes seen in present ECDSA and Schnorr schemes.
- The proposal combines stateful signatures utilizing Versatile XMSS and WOTS+C with a stateless fallback mechanism backed by SHA-256.
Charles Guillemet, Chief Know-how Officer at Ledger, warned that the Bitcoin quantum migration isn’t a right away {hardware} risk, however moderately a protracted technical coordination problem that might take years. The assertion was issued this Wednesday, September 16, following an analysis of the SHRINCS enchancment proposal.
By way of a technical publication, Guillemet famous that the present custody framework depends on digital signatures that will be compromised by a cryptographically related quantum laptop. A supply reported that the specialist argued ready for such {hardware} to emerge would symbolize an operational danger, given the intensive timeline required for analysis, testing, and network-wide deployment.
The evaluated framework, designated as SHRINCS, is a draft Bitcoin Enchancment Proposal (BIP) authored by Conduition, Ethan Heilman, Mikhail Kudinov, Oleksandr Kurbatov, Jonas Nick, and remix7531.
The structure depends completely on hash capabilities based mostly on SHA-256, the community’s native algorithm. In accordance with Guillemet’s evaluation, this design avoids introducing extra hardness assumptions—comparable to lattice-based cryptography—and targets Class 1 safety beneath the Nationwide Institute of Requirements and Know-how (NIST) requirements.
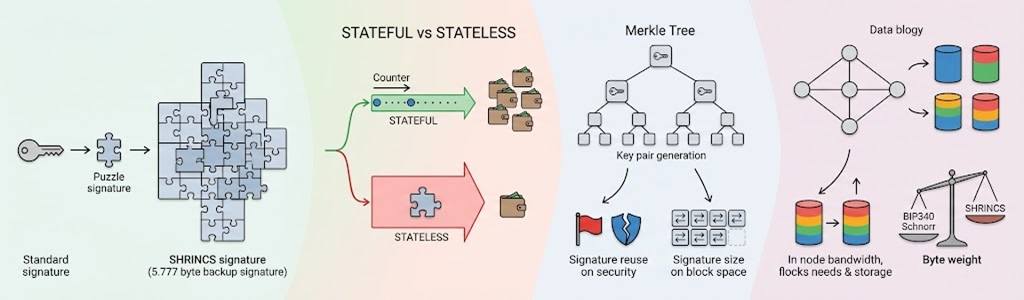
The draft’s technical specs set up a 48-byte public key. In distinction to Bitcoin’s present house effectivity, stateful signatures vary between 548 and 4,619 bytes, whereas the stateless fallback signature reaches 5,777 bytes.
Technical Challenges of SHRINCS and Pockets Administration
Implementing this scheme introduces unprecedented operational necessities for custodial software program and {hardware}. Based mostly on technical information examined by Guillemet, the compact pathway makes use of one-time keys structured in a Merkle tree, requiring the signer to keep up a persistent counter that by no means rolls again.
An unintended backup restore or concurrent signing occasion may set off cryptographic slot reuse, enabling third-party signature forgery. Within the occasion of state desynchronization or information loss, the seed phrase can generate a 5,777-byte stateless signature, shifting the trade-off towards block house consumption moderately than fund loss.
Moreover, findings within the evaluation counsel that hash-based key technology and stateless signature computation may take a number of minutes on up to date safe {hardware} units.
The mannequin additionally fails to protect unhardened derivation beneath BIP32 or the compact threshold signature schemes native to Schnorr. However, per-byte verification is computationally lighter than BIP340 Schnorr, because it consists primarily of SHA-256 operations. The chief famous that bigger transaction sizes will instantly affect community bandwidth, storage overhead, and the flexibility of on a regular basis customers to function full nodes.
Past algorithmic parameters, the transition presents main neighborhood governance dilemmas. In accordance with the report, attaining social consensus on the destiny of dormant cash whose public keys have by no means been uncovered to the blockchain looms as a much more advanced hurdle than choosing the mathematical normal itself.
Alongside this infrastructure debate, Ledger continues to navigate authorized challenges following a class-action lawsuit filed on August 27, 2026, within the U.S. District Courtroom for the Southern District of New York (Case 1:26-cv-07307-VM), the place plaintiffs search no less than $500 million in damages tied to prior information breaches. Technical discussions surrounding the SHRINCS draft will proceed throughout Bitcoin developer mailing lists, pending formal evaluations of its safety proofs.